Modern deanonymization techniques have rendered application-layer proxying insufficient, as sophisticated malware and misconfigured software frequently bypass local network settings to expose underlying IP addresses and hardware identifiers.
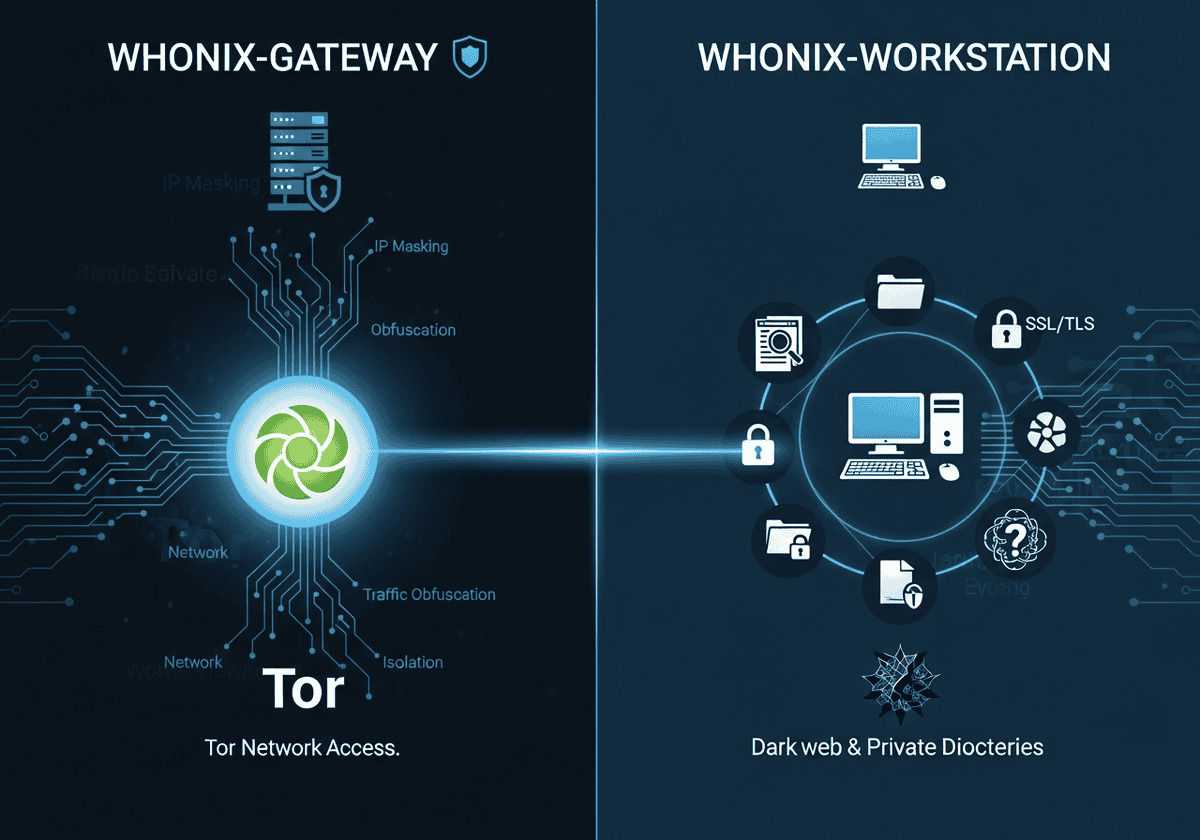
Whonix addresses these vulnerabilities through a dual-VM architecture that architecturally separates the network gateway from the user workstation, effectively eliminating IP leaks and DNS hijacking through mandatory Tor routing and application-level stream isolation.
This article provides a technical decomposition of the Whonix framework, focusing on its implementation of security through compartmentalization and the mitigation of side-channel attacks. We examine the underlying mechanisms used to prevent identity correlation and maintain a consistent anonymity profile across disparate sessions, evaluating the platform’s capacity to withstand advanced surveillance within a virtualized infrastructure.
Note this is an -in-depth article. The prior reading of these articles is recommended:
Key Take-Aways
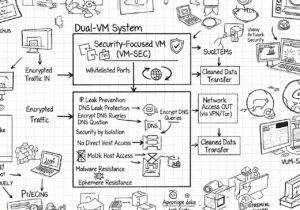
- Dual-VM architecture: separates the network gateway from the user workstation to prevent leaks.
- IP leak prevention: the workstation has no knowledge of your real IP address.
- Mandatory Tor routing: all workstation traffic is forced through the Tor network by the gateway.
- Security by isolation: compromising an application does not reveal your network identity.
- Secure time sync: uses sdwdate to prevent deanonymization via clock skew or time zones.
- Hardware masking: hides real hardware serial numbers and MAC addresses from the guest OS.
- DNS leak protection: automatically routes all DNS queries through the Tor network.
- Tor browser integration: includes a pre-configured Tor Browser for standardized web anonymity.
- Data persistence: designed to save files and configurations across reboots unlike amnesic systems.
- Malware resistance: root-level malware in the workstation cannot bypass the gateway’s Tor enforcement.
- No Tor over Tor: running a second Tor client inside the workstation is discouraged and risky.
Whonix in Short
Whonix is a specialized, Debian-based operating system designed for advanced anonymity and security through a unique dual-virtual machine (VM) architecture. Unlike standard privacy tools that run as applications within a host OS, Whonix splits its operations into two distinct components:
- the Whonix-Gateway: runs the Tor process and acts as a transparent proxy
- the Whonix-Workstation: provides a sandboxed environment for user activities such as web browsing, document editing, and communications.
These two VMs are linked via an isolated internal virtual network, ensuring that the Workstation has no direct path to the physical network interface of the host machine and can only communicate with the outside world through the Gateway’s Tor circuit.
The primary technical advantage of this design is the mitigation of “de-anonymization” attacks and DNS leaks. Because the Workstation is architecturally unaware of the host’s real IP address or MAC address, even a sophisticated malware infection with root privileges cannot “phone home” to reveal the user’s true identity.
Furthermore, Whonix implements Stream Isolation, which ensures that different applications (such as a web browser and an email client) use separate Tor circuits to prevent identity correlation. By forcing all traffic—including system updates and background processes—through the Tor network at the operating system level, Whonix provides a “fail-safe” environment that is significantly more robust than using the Tor Browser on a standard, non-hardened operating system.
Pros
| Cons
|
Whonix Alternatives

Selecting the appropriate privacy tool requires a clear understanding of whether your goal is simple data encryption, anonymous web browsing, or a comprehensive high-security environment.
The following comparison evaluates VPNs, the Tor Browser, and Whonix across key metrics like anonymity, leak protection, and ease of use to help you identify the best solution for your specific needs:
| VPN (Virtual Private Network) | Tor Browser | Whonix (Operating System) | |
| Primary Goal | Privacy & Geo-spoofing | Anonymity & Censorship Circumvention | Maximum Security & Leak Prevention |
| How it Works | Routes traffic through a single encrypted “tunnel” to a server owned by a provider. | Routes traffic through 3 random layers of volunteer nodes (Entry, Middle, Exit). | A “Gateway” VM forces all OS traffic through Tor; a “Workstation” VM runs the apps. |
| Anonymity Level | Low to Medium. The VPN provider knows your real IP and can see your traffic. | High. No single node knows both your IP and your destination. | Very High. Designed to prevent “de-anonymization” even if the browser is hacked. |
| IP Leak Protection | Basic. If the VPN drops, your real IP may leak (unless a “Kill Switch” is used). | Good. Only protects traffic inside the browser. Other apps leak your real IP. | Total. It is architecturally impossible for the Workstation to see your real IP. |
| Speed | Fast. Suitable for 4K streaming, gaming, and large downloads. | Slow. Traffic bounces around the world, causing high latency, limited by the speed of the Tor network. | |
| Ease of Use | Very Easy. One-click “Connect” apps for all devices. | Easy. Works like a standard web browser (Firefox-based). | Difficult. Requires VirtualBox/KVM and knowledge of Virtual Machines. |
| Trust Model | Centralized. You must trust the VPN provider not to log your data. | Decentralized. You don’t have to trust any single person or entity. | Decentralized. Built on Tor and Open Source Linux (Debian). |
| Cost | Usually Paid for reputable “No-Log” services. | Free. | Free. |
… with Qubes OS ?
The fundamental difference between Qubes OS and Whonix lies in their primary security objectives:, while
- Qubes OS focuses on security through isolation: a “Type-1” hypervisor-based operating system that allows a user to compartmentalize their digital life into separate virtual machines (qubes), such as “work,” “personal,” and “banking.” If one qube is compromised by malware, the isolation ensures the attacker cannot access the data in other qubes.
- Whonix focuses on anonymity through torification: specialized configuration of two VMs designed specifically to hide a user’s IP address and prevent network-level tracking.
While Qubes protects the integrity of your local data across different contexts, Whonix protects your identity from the external internet.
The two systems reach their full potential through a deep technical complementarity known as Whonix-on-Qubes: in this integration, Whonix is not run inside a third-party application like VirtualBox; instead, it is baked directly into the Qubes ecosystem as a set of “TemplateVMs.” Qubes replaces the standard Linux networking stack with a Whonix-Gateway ProxyVM, which forces all traffic from a designated Whonix-Workstation AppVM through the Tor network.
This setup is significantly more secure than the standard Whonix installation because Qubes utilizes the Xen hypervisor, which is much harder to “break out” of than consumer-grade virtualization software. This creates a layered defense where Qubes provides the “walls” between tasks and Whonix provides the “cloak” for the network traffic.
Beyond simple integration, the combination of these two platforms enables advanced security workflows that neither could achieve alone, most notably Disposable Whonix VMs. In Qubes, a user can launch a Whonix-Workstation that exists only for a single session; the moment the application or VM is closed, the entire environment—including any malware or forensic traces—is instantly deleted from the system. This provides the “amnesic” qualities of Tails (a live OS) with the persistent, high-isolation hardware security of Qubes.
Summary: When to Use Whonix

- You are a journalist, whistleblower, or researcher dealing with high-risk information.
- You are worried about malware that might try to “phone home” and reveal your real IP address.
- You need to use applications other than a browser (like an email client or chat app) anonymously.
Verdict: best for maximum security and professional-grade anonymity.
For text chat over Tor, a free irc client configured on the Workstation, or an online irc client opened in the browser, can reach IRC networks without exposing the real address. Newcomers can start with a few irc commands such as join and msg, and read how to use irc before connecting.
FAQ
What is the core architecture of Whonix?
Whonix uses a dual-VM design consisting of a Gateway that handles all Tor connections and a Workstation for user applications. This separation ensures that the Workstation never knows the user’s real IP address or hardware serial numbers.
How does Whonix prevent IP leaks even if an application is compromised?
Since the Workstation has no direct access to the internet and can only communicate through the Gateway, even root-level malware cannot discover or broadcast your real IP. All traffic is forcibly routed through the Tor network by the Gateway’s firewall rules.
Why does Whonix use two separate virtual machines instead of one?
Using two VMs creates a “security by isolation” barrier that prevents network-level leaks and local hardware identification. If the application layer in the Workstation is breached, the network layer in the Gateway remains isolated and secure.
Can I use Whonix if my host operating system is infected with malware?
No, because the host operating system and its hypervisor have total control over the virtual machines. If the host is compromised, an attacker can log keystrokes, take screenshots, or manipulate the Whonix VMs directly.
How is Whonix different from the Tails operating system?
Tails is a live “amnesic” OS designed to leave no trace on a computer’s hard drive, while Whonix is designed for persistent use within a virtualized environment. Whonix offers stronger protection against certain types of de-anonymization attacks due to its split-VM architecture.
Is it safe to use a VPN with Whonix?
While possible, adding a VPN increases complexity and can potentially introduce new attack vectors or “tunnel vision” risks. It is generally only recommended for advanced users who need to hide Tor usage from their ISP or access services that block Tor.
What is “Stream Isolation” and why is it important in Whonix?
Stream isolation forces different applications to use separate Tor circuits so that their traffic cannot be easily correlated by an exit node. This prevents an observer from linking your web browsing session to your background email syncing or other activities.
Why is the system time in Whonix different from my local time?
Whonix uses UTC and a tool called sdwdate to synchronize time securely via onion services rather than insecure NTP servers. This prevents “time attacks” where an adversary uses clock skew or local time zones to identify your physical location.
Can I run Whonix on a USB drive like Tails?
Whonix is not primarily designed as a live bootable USB, though it can be installed on an external drive and run via a host OS. For a true “plug-and-play” amnesic experience on any hardware, Tails remains the standard choice.
Does Whonix protect me from browser fingerprinting?
Whonix includes the Tor Browser, which is specifically patched to provide a uniform fingerprint shared by millions of other users. By running it within the standardized Workstation environment, you further reduce the unique hardware identifiers available to websites.
Why is it discouraged to run a Tor client inside the Whonix-Workstation?
Running “Tor over Tor” creates a nested circuit that significantly degrades performance and can lead to unpredictable routing behavior. It does not provide “double anonymity” and may actually make your traffic patterns more distinct to network observers.
Related Readings & Concepts (experts)
- Tor network: a decentralized anonymity network that routes your traffic through three random relays to conceal your identity and location from observers.
- Virtualization: the technology used to run Whonix’s two-VM architecture, providing a layer of separation between the guest operating systems and your physical hardware.
- Operational Security (OpSec): the set of habits and procedures you must follow to prevent revealing your identity through behavioral patterns or accidental data leaks.
- Pseudonymity: the use of a persistent but non-identifying alias, which requires careful management in Whonix to avoid linking different online identities together.
- Stream isolation: a feature that forces different applications to use different Tor circuits, preventing an observer from correlating your activities across various services.
- Transparent Proxying: a mechanism where the Gateway automatically intercepts and routes all Workstation traffic through Tor, even for applications not natively configured for it.
- DNS leak: a security flaw where your domain name requests bypass the anonymity network, potentially revealing your browsing history to your ISP.
- IP leak: a critical failure where your real, deanonymizing IP address is exposed to a destination server or an eavesdropper.
- Browser fingerprinting: a tracking technique that identifies you based on unique browser configurations, which Whonix mitigates by providing a standardized environment.
- Tor over Tor: a problematic configuration where a Tor client is run inside a system already routed through Tor, which can lead to performance issues and unpredictable security risks.
- Tor bridges: private Tor relays that are not listed in the public directory, used to bypass censorship in regions where the Tor network is blocked.
- Entry guards: the first relays in a Tor circuit that are specifically chosen for their long-term stability to protect users against certain types of deanonymization attacks.
- Onion services: websites or services that end in .onion and are hosted entirely within the Tor network, providing end-to-end encryption and metadata protection.
- Identity correlation: the risk of an adversary linking different sessions or accounts to the same person by observing shared identifiers or consistent behavioral traits.
External Links on Whonix
International Standards
- ISO/IEC 27001:2013 Information technology -- Security techniques -- Information security management systems -- Requirements
- ISO/IEC 27002:2013 Information technology -- Security techniques -- Code of practice for information security controls
- NIST SP 800-53 Rev. 5 Security and Privacy Controls for Information Systems and Organizations
(hover the link to see our description of the content)