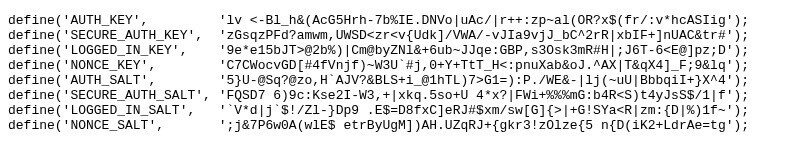
The WordPress Secret Key API generates a set of unique cryptographic salts and keys—specifically AUTH, SECURE_AUTH, LOGGED_IN, and NONCE—to secure application configurations.
These keys provide high-entropy random data that is combined with user credentials and session cookies before hashing, effectively neutralizing the threat of rainbow table attacks and pre-computed hash cracking. By delivering a fresh set of random strings upon every request, the service ensures that authentication tokens remain unique to the specific environment, hardening the application against unauthorized session access.
An extremely simple tool to use: just visit the page and have directly all the keys to copy/paste into your wp-admin.php file. New keys at every page reload. No option to select, nothing else. Efficient!
It is provided by the WordPress original team. It is recommended to change your key salts from time to time (note that this will log-out all connected users and on-going activities and cookies … which is one of the goal btw).




















