Product Design, Manufacturing & Innovation Resources
Home » Online Tools » Security Headers Tester

Security Headers Tester

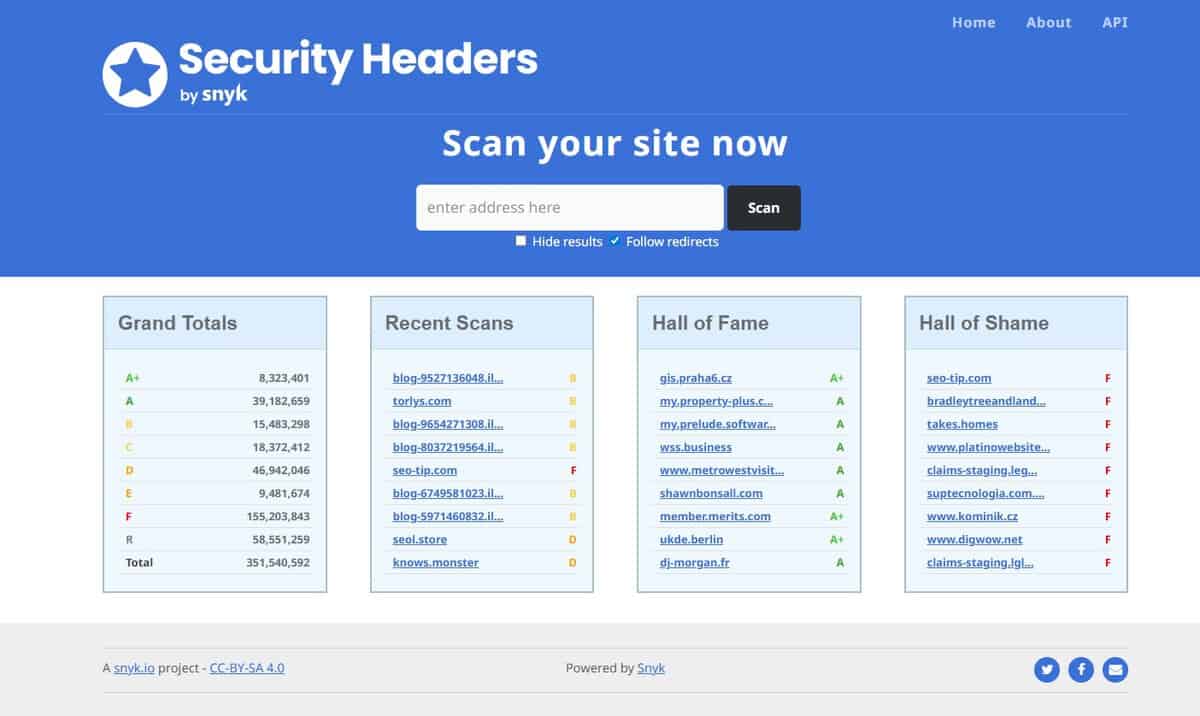
Just provide any URL or domain and it will analyse the headers served by the given page. Among many header tested: HTTP Strict-Transport-Security (HSTS), Content-Security-Policy (CSP), X-Frame-Options,  X-Content-Type-Options, Referrer-Policy, Permissions-Policy, Cross-Origin-Opener-Policy (COOP), Cross-Origin-Resource-Policy (CORP), Set-Cookie, Access-Control-Allow-Origine …

Very complete and useful for

  • Site owners: to check their setup and how their site is viewed by browsers, crawler, bots, so as customer (and their related trust). A must for big brands and commercial sites.
  • Visitors or shoppers: wanting to know your policy and risk of browsing your site. A must if you already have some doubts (but in general, for safety or security, you know the saying “if you already have a doubt …”).

Not only a very good tool, but also the documentation and examples along with each header type is of great help.

Be prepared: if your site is heavily depending on several external ressources providers (font, scripts, CDNs, external cookies, embeds ..), it will be very hard to get the “A+” grade, mainly due to the “Content Security Policy” and its optimal requirement (loading everything locally, https, trusted sources …)

Note: mind if you check or not the box “hide results” … as your results:

  • will be public
  • and could be included in either the “Hall of Fame” or the “All of Shame” (that being said, it is maybe a chance to get a link for SEO purposes …)

Recommended!
Disciplines: Cybersecurity, Web development, DevOps, Compliance, IT administration.
Free alternative to MDN HTTP Observatory, Qualys SSL Labs.
Security Headers Tester compared with MDN HTTP Observatory and Qualys SSL Labs
Security Headers TesterMDN HTTP ObservatoryQualys SSL Labs
What is tested: The tool analyses the HTTP response headers of a page, such as Strict-Transport-Security, Content-Security-Policy, X-Frame-Options and Referrer-Policy.What is tested: The HTTP Observatory tests headers such as CSP and HSTS, insecure cookies, the order of HTTP to HTTPS redirects and Cross-Origin-Resource-Policy. It does not test outdated software, SQL injection or CMS plugins, and the current version has no TLS analysis.What is tested: SSL Labs tests the SSL/TLS configuration of public web servers. It checks that the certificate chain is trusted and looks for configuration weaknesses and performance problems.
Grading: Grades run from A+ to F, with an additional R grade. Sites are also listed in Hall of Fame and Hall of Shame tables.Grading: A grade such as A+ comes with a numeric score. The FAQ warns that an A+ does not mean a site is secure, since many issues are outside the scanner scope.Grading: Ratings run from A+ to F, with a numeric score across several categories.
Visibility of results: A Hide results option is offered on the scan form, which keeps a scan out of the public lists.Visibility of results: The scan history of each domain is public, and no per-scan visibility option remains. The service does not store user data tied to individual scans.
API: The navigation lists an API section with API keys, terms and documentation.API: A v2 endpoint accepts a POST request with the host name and returns the grade, score and test counts as JSON. A site can be rescanned at most once every 60 seconds.
Owner and cost: The tool was created by Scott Helme and is now part of Snyk. It is free to use.Owner and cost: The service is run by Mozilla and launched in 2016. The landing page reports more than 47 million scans.Owner and cost: The service is free and comes from Qualys. Its creator described it as a non-commercial research effort.

Topics covered: Security Headers Tester, HTTP Strict-Transport-Security, Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, Cross-Origin-Opener-Policy, Cross-Origin-Resource-Policy, Set-Cookie, Access-Control-Allow-Origin, site owners, visitors, risk assessment, external resources, documentation, SEO ISO/IEC 27001, ISO/IEC 27002, OWASP ASVS, NIST SP 800-53, and RFC 6797..

More Network & Web tools

Suggest your best online tool:

Do you know a better, a complementary or a replacement website to the one listed above ?

> Suggest it here <

10th year anniversary

Full size images and downloads are only available, 100% free, for registered members.

> Login <