Product Design, Manufacturing & Innovation Resources

تحليل شجرة الخطأ (FTA)

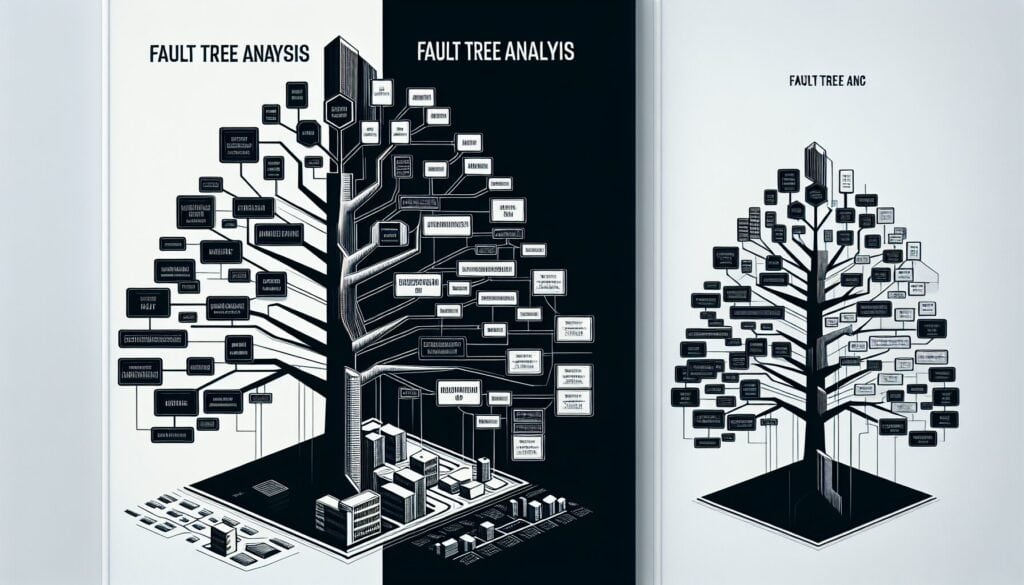
Fault Tree Analysis

تحليل شجرة الخطأ (FTA)

Objective:

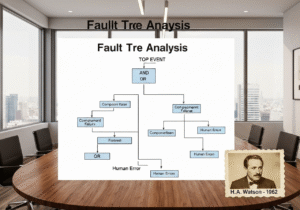
A top-down, deductive failure analysis technique where an undesired state of a system (the “top event” or failure) is analyzed using Boolean logic to combine a series of lower-level events or failures that could cause it.
How it’s used:

الايجابيات

سلبيات

Categories:

الأفضل لـ:

تحليل شجرة الأعطال (هيئة النقل المجانية) is particularly advantageous in industries such as aerospace, automotive, nuclear power, and healthcare, where system reliability and safety are paramount. This methodology is effective during the design phase of a project, where engineers and designers can preemptively identify potential failure modes before they manifest in real-world applications. For example, in the aerospace sector, FTA can be employed to analyze the reliability of a التحكم في الطيران system, mapping out all possible failure pathways that could lead to a flight safety incident. In the automotive industry, manufacturers might utilize FTA when developing new vehicle models to ensure that all safety mechanisms are robust against potential failure scenarios. Participants in an FTA typically include system engineers, safety engineers, and reliability analysts, who collaboratively assess both hardware and software components of a system. It is often initiated by stakeholders seeking to improve operational safety and reduce risks associated with system failures. By quantifying the probabilities of basic events, FTA also enables organizations to allocate resources effectively, directing focus to the most significant risk factors that, if addressed, would yield substantial improvements in safety and reliability metrics. The visual representation of the fault tree further facilitates communication among multidisciplinary teams and supports decision-making processes by providing clear pathways that depict how various failures can converge to a top event. This structured approach aligns well with regulatory requirements in industries governed by strict safety standards, ultimately leading to enhanced compliance with safety protocols.

Key steps of this methodology

  1. حدد الحدث الرئيسي الذي يمثل فشل النظام.
  2. حدد الأسباب المباشرة التي قد تؤدي إلى الحدث الرئيسي.
  3. قم بتطوير أحداث وسيطة تساهم في الأسباب المباشرة.
  4. قم بربط الأحداث باستخدام البوابات المنطقية (AND، OR) لتوضيح العلاقات.
  5. قم بتعيين احتمالات للأحداث الأساسية حيثما أمكن ذلك.
  6. احسب احتمالية وقوع الحدث الأعلى باستخدام احتمالات الأحداث الأساسية.
  7. قم بمراجعة شجرة الأعطال وتحسينها لضمان اكتمالها ودقتها.

نصائح احترافية

  • دمج تحليل تأثيرات أنماط الفشل (تحليل الوضع والتأثير والتأثير) مع تحليل أنماط الفشل (FTA) لفهم شامل لأنماط الفشل وتأثيراتها على أداء النظام.
  • استخدم تحليل الحساسية على الاحتمالات المخصصة للأحداث الأساسية لتحديد الأحداث التي تؤثر بشكل كبير على احتمالية الحدث الأعلى.
  • قم بتحديث شجرة الأعطال بانتظام مع تطور تصميمات النظام أو مع توفر البيانات التشغيلية لضمان الملاءمة والدقة في تقييمات المخاطر.

To read and compare several methodologies, we recommend the

> Extensive Methodologies Repository  <
together with the 400+ other methodologies.

Your comments on this methodology or additional info are welcome on the comment section below ↓ , so as any engineering-related ideas or links.

السياق التاريخي

1960
1960
1960
1962
1963
1965-12-21
1970
1960
1960
1960
1960
1962-10-09
1964
1970
1970

(إذا كان التاريخ غير معروف أو غير ذي صلة، على سبيل المثال "ميكانيكا الموائع"، يتم توفير تقدير تقريبي لظهوره الملحوظ)


أحدث الإضافات

أهم المنشورات والمقالات

أفضل الأدوات الأصلية

السنة العاشرة عيد

الصور والتنزيلات بالحجم الكامل متاحة فقط، ومجانية تمامًا، للأعضاء المسجلين.