Product Design, Manufacturing & Innovation Resources
집 » 온라인 도구 » Pwned 이메일 유출 테스트 도구

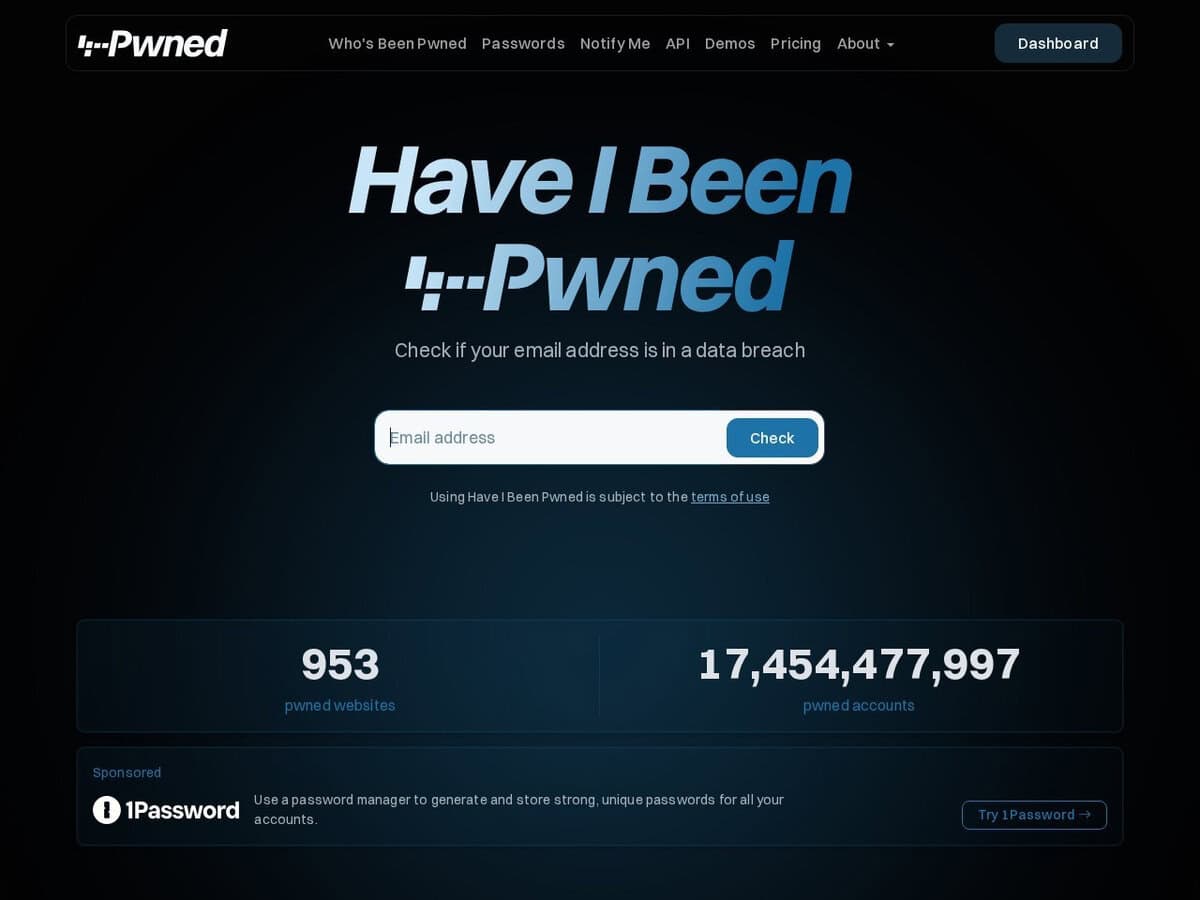
Pwned 이메일 유출 테스트 도구

Have I Been Pwned(HIBP)는 알려진 인터넷 유출 또는 데이터 침해 데이터베이스를 기반으로 이메일을 검사하여 이메일 주소나 기타 민감한 개인 정보가 노출되었는지 확인합니다. HIBP는 데이터 침해 정보를 집계하는 중앙 집중식 저장소 역할을 하며, 공개된 유출 정보와 악성코드에 의한 탈취 로그에서 수집한 140억 개 이상의 고유 기록을 색인화합니다. 이 플랫폼을 통해 사용자는 알려진 침해 사례와 이메일 주소 및 전화번호를 대조하여 비밀번호, 실제 주소, IP 주소 기록 등 노출된 특정 데이터 유형을 식별할 수 있습니다. 조직 보안을 위해 자동화된 자격 증명 검사를 위한 RESTful API와 관리자가 평문 비밀번호를 저장하지 않고도 전체 기업 네임스페이스의 시스템적 노출 여부를 모니터링할 수 있는 도메인 검색 기능을 제공합니다.

만약 여러분이 이메일을 몇 년 동안 사용해왔다면, 유출 사고에 연루되지 않았다는 건 오히려 놀라운 일일 겁니다. 저희 테스트 결과, 저희 이메일 계정은 2~10건의 유출 사고에 연루되었습니다. 따라서 이러한 사실을 확인하는 것이 중요합니다. 또한 유출 사고 목록과 세부 정보도 매우 흥미롭습니다.

HIBP는 디지털 공급망을 확보하고 독점 정보를 보호하는 데 적용될 수 있습니다. intellectual property이러한 분야의 전문가들은 다음과 같은 목적으로 해당 서비스를 활용할 수 있습니다.

  • Pwned Passwords API를 산업 제어 시스템(ICS)의 인증 시스템에 통합하여 알려진 유출된 자격 증명의 사용을 차단하십시오.
  • 기업 스파이 행위 및 민감한 연구 개발 데이터 또는 독점 설계의 도난 위험을 완화하기 위해 엔지니어링 및 연구팀의 기업 신원을 감사합니다.
  • 기업 네트워크 내에서의 수평 이동이나 시뮬레이션 환경에 대한 무단 접근을 용이하게 할 수 있는 자격 증명 유출에 대해 혁신 허브를 모니터링하십시오.
  • 제3자 공급업체 및 계약업체가 엄격한 자격 증명 관리 절차를 준수하도록 함으로써 품질 보증 표준을 유지하고, 이를 통해 랜섬웨어로 인한 생산 중단 위험을 줄입니다.

분야: 사이버 보안, 개인정보 보호, IT 관리, OSINT.
Free alternative to DeHashed, Mozilla Monitor.
Have I Been Pwned compared with DeHashed and Mozilla Monitor
Have I Been PwnedDeHashedMozilla Monitor (now Mozilla Monitor)
Function and data source: Checks email addresses and phone numbers against known breaches, and offers domain search for verified domains and the Pwned Passwords service.Function and data source: A personal asset search engine over data posted on the clear and deep web, with lookups for usernames, emails and IP addresses. It returns the exposed data itself, as well as notifying about breaches.Function and data source: The service was renamed Mozilla Monitor. It scans for exposure of an email address, and Mozilla states that its breach data comes from Have I Been Pwned.
API and automation: Breached account, paste, domain and stealer log queries need a 32-character API key sent in the hibp-api-key header. Pwned Passwords needs no key and uses k-anonymity: only the first 5 characters of a SHA-1 hash are sent.API and automation: An API is offered for programmatic breach-data queries. Its pricing page does not state whether API access is part of a plan.
비용 모델: API tiers are Core, Pro and High RPM, and stealer log queries require Pro or higher. Prices are on the pricing page, which could not be read here.비용 모델: Paid plans are listed for 7 days, one month and one year, with unlimited asset searches in each plan.비용 모델: Described as free. A public breach search works without an account, while future alerts and the detailed report need a Mozilla account.
Licence and verification: The breach and paste APIs are under CC BY 4.0, which requires crediting Have I Been Pwned with a link. Domain search requires proving control by a DNS TXT record or an approval email to one of five aliases (admin, hostmaster, info, security, webmaster).Licence and verification: Users can opt an email out of the underlying Have I Been Pwned database through its opt-out page.

다룬 주제: 이메일 유출 테스트, 데이터 유출, 손상된 자격 증명, 민감한 개인 정보, HIBP, 중앙 집중식 저장소, RESTful API, 자격 증명 확인, 도메인 검색, 디지털 공급망, 기업 스파이 행위, 독점적 지적 재산, Pwned Passwords API, 산업 제어 시스템, 혁신 허브, 자격 증명 관리, 품질 보증 및 랜섬웨어.

은둔: 저희는 이 도구나 제작자와 관련된 잠재적인 문제점에 대한 피드백을 받지 못했습니다. 하지만 많은 온라인 서비스와 마찬가지로, 사용자는 자신의 데이터를 직접 제공하고 있습니다. 데이터의 중요도에 따라 제작자의 평판과 오용 가능성을 판단하고, 이용 약관을 확인하고 동의할지 여부를 결정하는 것은 사용자의 책임입니다.

더 네트워크 및 웹, OSINT tools

가장 유용한 온라인 도구를 추천해 주세요:

위에 소개된 웹사이트보다 더 나은, 보완적인 또는 대체할 만한 웹사이트를 알고 계신가요?

> 여기에 제안해 주세요 <

10년차 기념일

고화질 이미지 및 다운로드는 등록된 회원에게만 100% 무료로 제공됩니다.

> 로그인 <